5 min read

Choosing a cloud service provider is a major decision for many organizations, especially when you factor in FedRAMP compliance. Understanding the levels of FedRAMP compliance is imperative for those agencies trying to determine which cloud service provider is right for their needs.
Update, October 2026: FedRAMP has renamed this status. When the FedRAMP Consolidated Rules for 2026 (CR26) took effect on July 4, 2026, following public comment on RFC-0020 in early 2026, “FedRAMP Authorization” became “FedRAMP Certification.” In later posts you’ll see Sharetru Federal described as FedRAMP Rev 5 (Class C) Certified: the same FedRAMP Moderate status under its new name.
So, what is FedRAMP? According to the United States government, “The Federal Risk and Authorization Management Program (FedRAMP) is a government-wide program that provides a standardized approach to security assessment, authorization, and continuous monitoring for cloud products and services.” Basically, it’s the security measures that all cloud service providers should have in place to attain the appropriate authorizations.In this article, you’ll learn more about FedRAMP, the different impact levels associated with FedRAMP compliance, and the considerations organizations should make before adopting a cloud service provider.
FedRAMP: What You Should Know
As the world’s reliance on digital data increased (and in anticipation of future digital dependence), the U.S. government recognized a need for data security standardization across agencies entrusted with government data. While The E-Government Act of 2002 established FISMA, or the Federal Information Security Management Act, there was eventually a need to protect data in the cloud. Thus, FedRAMP was established in 2011.
FedRAMP outlined data security standards that could be applied across all federal agencies for greater protection of sensitive data. It also provided guidelines on conducting security assessments and how to protect data, specifically data stored on cloud-based applications. Broadly, FedRAMP filled in FISMA gaps and addressed new and evolving technology used by federal agencies.
FedRAMP was designed to provide federal agencies with repeatable, efficient, cost-effective security processes to ensure data was protected by Cloud Service Providers (CSPs). The security measures proposed by FedRAMP are not a “once and done” compliance activity. You must invest ongoing time and effort into maintaining FedRAMP compliance.
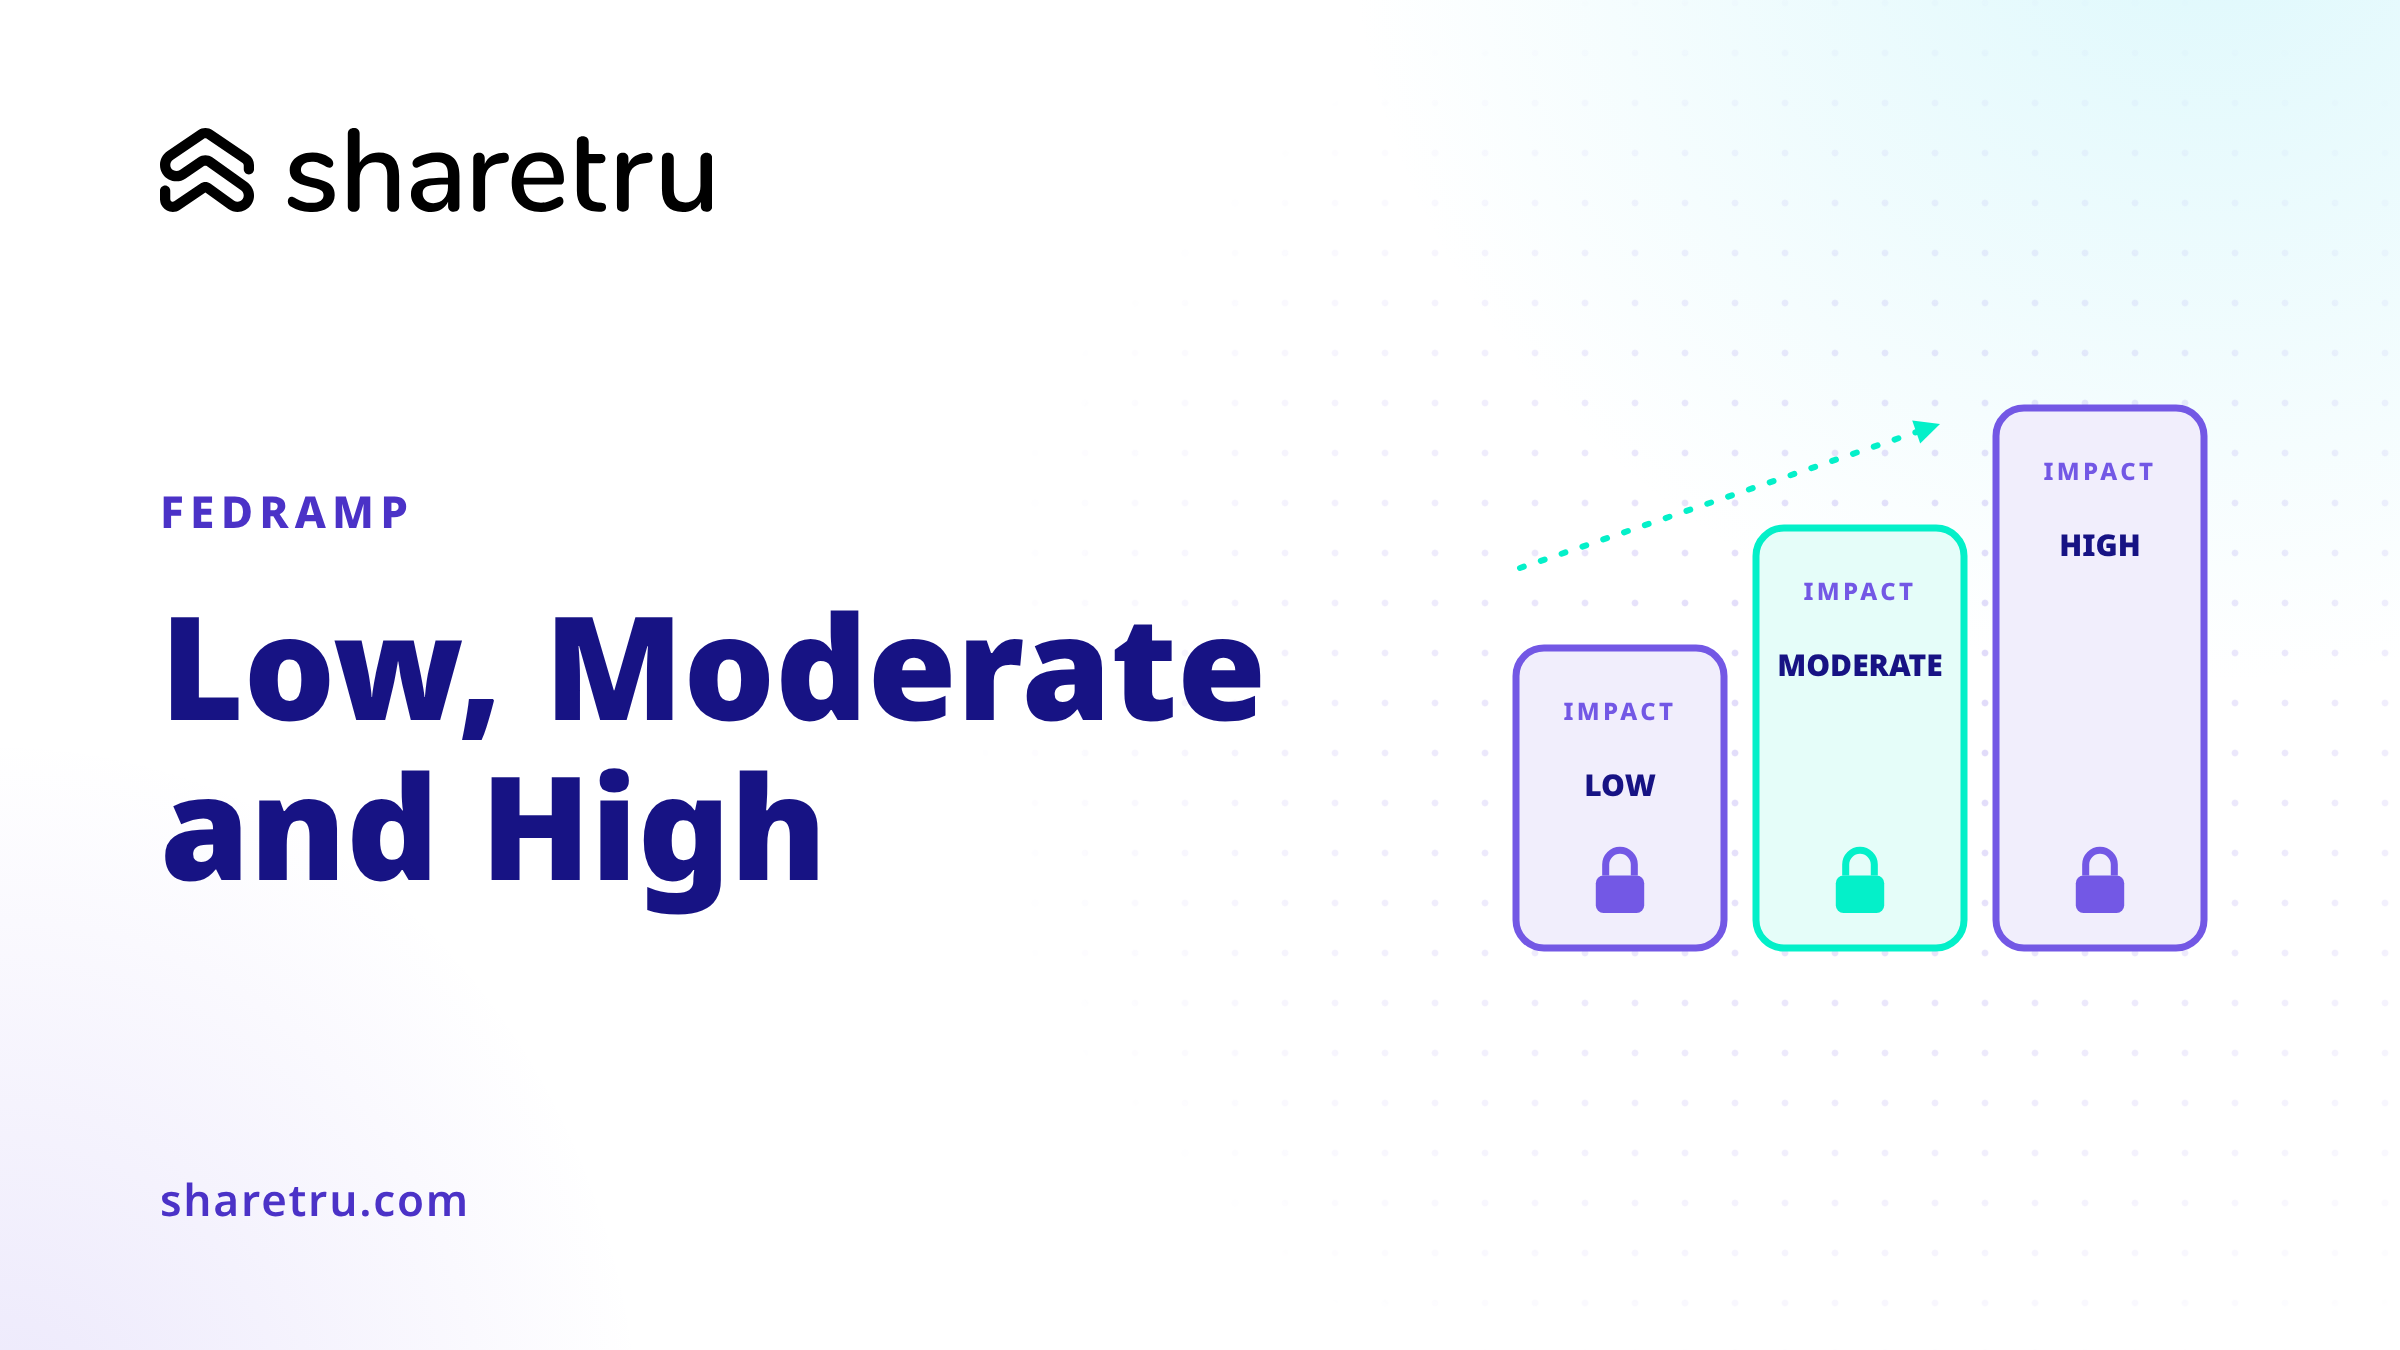
To differentiate between the security controls organizations can expect from CSPs, FedRAMP categorizes different CSPs based on the security measures they have in place. By dividing CSPs into three different categories – low, moderate, and high impact – organizations can determine which solutions are best suited to their data protection needs. Each impact level is viewed through the lens of the following three FedRAMP security objectives:
- Confidentiality - data remains confidential
- Integrity - data integrity is maintained, avoiding data alteration or destruction
- Availability - Vital data is readily available
To ensure your CSP is meeting these objectives and maintaining FedRAMP-compliant security standards, let’s learn more about the three levels of data security impact.

Low Impact Level
Do you primarily use data that is publicly available? Working with a low-impact level CSP could be right for your needs. A Low Impact Software as a Service (LI-SaaS) is the best fit for an organization where compromises to data confidentiality, integrity, and availability would have minimal impact on your organization, employees, clients, or the federal government.
Consider this to be low-stakes in terms of data security standards. However, some basic, common-sense security standards do apply. (Explore the Controls Guide for more information.) To identify if a CSP is an LI-SaaS, FedRAMP has provided a list of questions for you to consider. If the answer to all of the following is yes, this is an LI-SaaS:
- Is this a cloud-based service?
- Is this a fully operational service?
- Is this a SaaS (Software as a Service)? (Look to NIST SP 800-145, The NIST Definition of Cloud Computing for more details.)
- Is the only personal information contained by the SaaS limited to login information (username, email, password)?
- Is this a low-security-impact SaaS? (Look to FIPS PUB 199: Standards for Security Categorization of Federal Information and Information Systems for more details.)
- Are you providing the underlying cloud infrastructure or is the SaaS hosted by a FedRAMP-authorized Platform like Service (PaaS) or Infrastructure as a Service (IaaS)?
If you answered yes to these questions, this is an LI-SaaS, and if you have minimal security needs, a low-impact level CSP could be the best fit for your organization.
Moderate Impact Level
Moderate Impact level systems have slightly higher standards when it comes to data security. So, if you handle sensitive data that, if compromised, could lead to serious consequences, you should consider only using CSPs that adhere to the Moderate Impact Controls Guide.
CSPs with Moderate Impact security controls account for about 80% of total CSP applications that receive FedRAMP authorization. So, this means Moderate Impact CSPs are likely to meet the needs of most organizations.
What kind of data does Moderate Impact CSPs protect? This is data used by agencies that are not generally available to the public. While this is not data considered to be “top secret,” a data security breach dealing with this type of data could have somewhat severe consequences for clients, employees, the government, or the organization itself.
High Impact Level
Finally, High Impact level CSPs deal with the most sensitive data used by government agencies. Some common organizations that require High Impact CSPs are:
- Law Enforcement Agencies
- Emergency Service Systems
- Financial Services
- Healthcare Systems
These organizations handle the most sensitive types of data, and if this data were to fall in the wrong hands, the consequences could be severe. If your organization handles this type of data, it’s imperative that you only adopt cloud-based solutions that have the appropriate security controls in place. FedRAMP outlines a staggering 421 security controls in the High Impact Controls Guide for CSPs that receive this level of authorization.
Before you adopt your next cloud solution, it’s important to understand how FedRAMP could impact your decision. Carefully consider the type of data you handle, and choose a CSP that falls into the appropriate FedRAMP compliance category.
Learn more about compliance measures that could impact your business. Download this free ITAR compliance guide now.

Related articles
All articles
5 Tips for Using the FedRAMP Marketplace
The FedRAMP Marketplace is a helpful resource for federal agencies looking for FedRAMP compliant cloud vendors, products, agencies, …
What are the Costs of Working with a FedRAMP Authorized CSP?
Working with a FedRAMP Authorized cloud service provider (CSP) is required for federal government agencies. Federal Risk and Authorization …
Understanding the Basics of FedRAMP Compliance
The Federal Risk and Authorization Management Program (FedRAMP) essentially is a standardized approach to securing online cloud platforms. …
