5 min read

Last week, the CMMC community gathered at the Gaylord National Resort & Convention Center in National Harbor, Maryland, for CS5 East 2026, the official conference of The Cyber AB. Sharetru was there as a VIP exhibitor at Booth #7, and our CEO, Brendon Ainsworth, and I spent October 22–23 talking with defense contractors, assessors, and partners about a question on a lot of minds this year: with CMMC paused, what still has to happen to protect CUI?
Thank you to everyone who stopped by the booth. If we missed each other, here's a quick look at the event, why protecting CUI matters even more right now, and how Sharetru can help.
What is CS5 East?
CS5 East is The Cyber AB's conference for the CMMC ecosystem, billed as "the essential gathering for Defense Contractors and their Subcontractors to get CMMC compliance right." It brings together organizations seeking CMMC certification, Registered Practitioner Organizations (RPOs), Certified Third-Party Assessor Organizations (C3PAOs), MSPs, MSSPs, cloud providers, and the compliance and IT leaders who support them.
This year's program included:
- General sessions with The Cyber AB, DoD officials, and industry leaders
- A two-day Contractor Track covering SSP development through assessment prep
- A mock CMMC assessment
- CCP, CCA, and executive training
- Express Connect 1:1 matchmaking with solution providers
- An exhibit hall with 80+ vendors
For the full agenda and details on future events, visit cs5east.org and the CS5 East agenda.
CMMC is paused. Protecting CUI is not.
The timing made this year's conversations different. In July, DoD suspended the CMMC Phase 2 third-party certification requirements and stood up a CMMC Reform Task Force to review the program. As Brendon wrote in CMMC Phase 2 Just Got Suspended. Your Obligation to Protect CUI Did Not., the pause changed how compliance gets verified. It didn't change whether you have to protect CUI.
DFARS 252.204-7012 is still in your contract. It still requires you to safeguard covered defense information in line with NIST SP 800-171, and it still requires any cloud service provider that stores, processes, or transmits that information for you to meet the FedRAMP Moderate baseline. Phase 1 self-assessments haven't moved either.
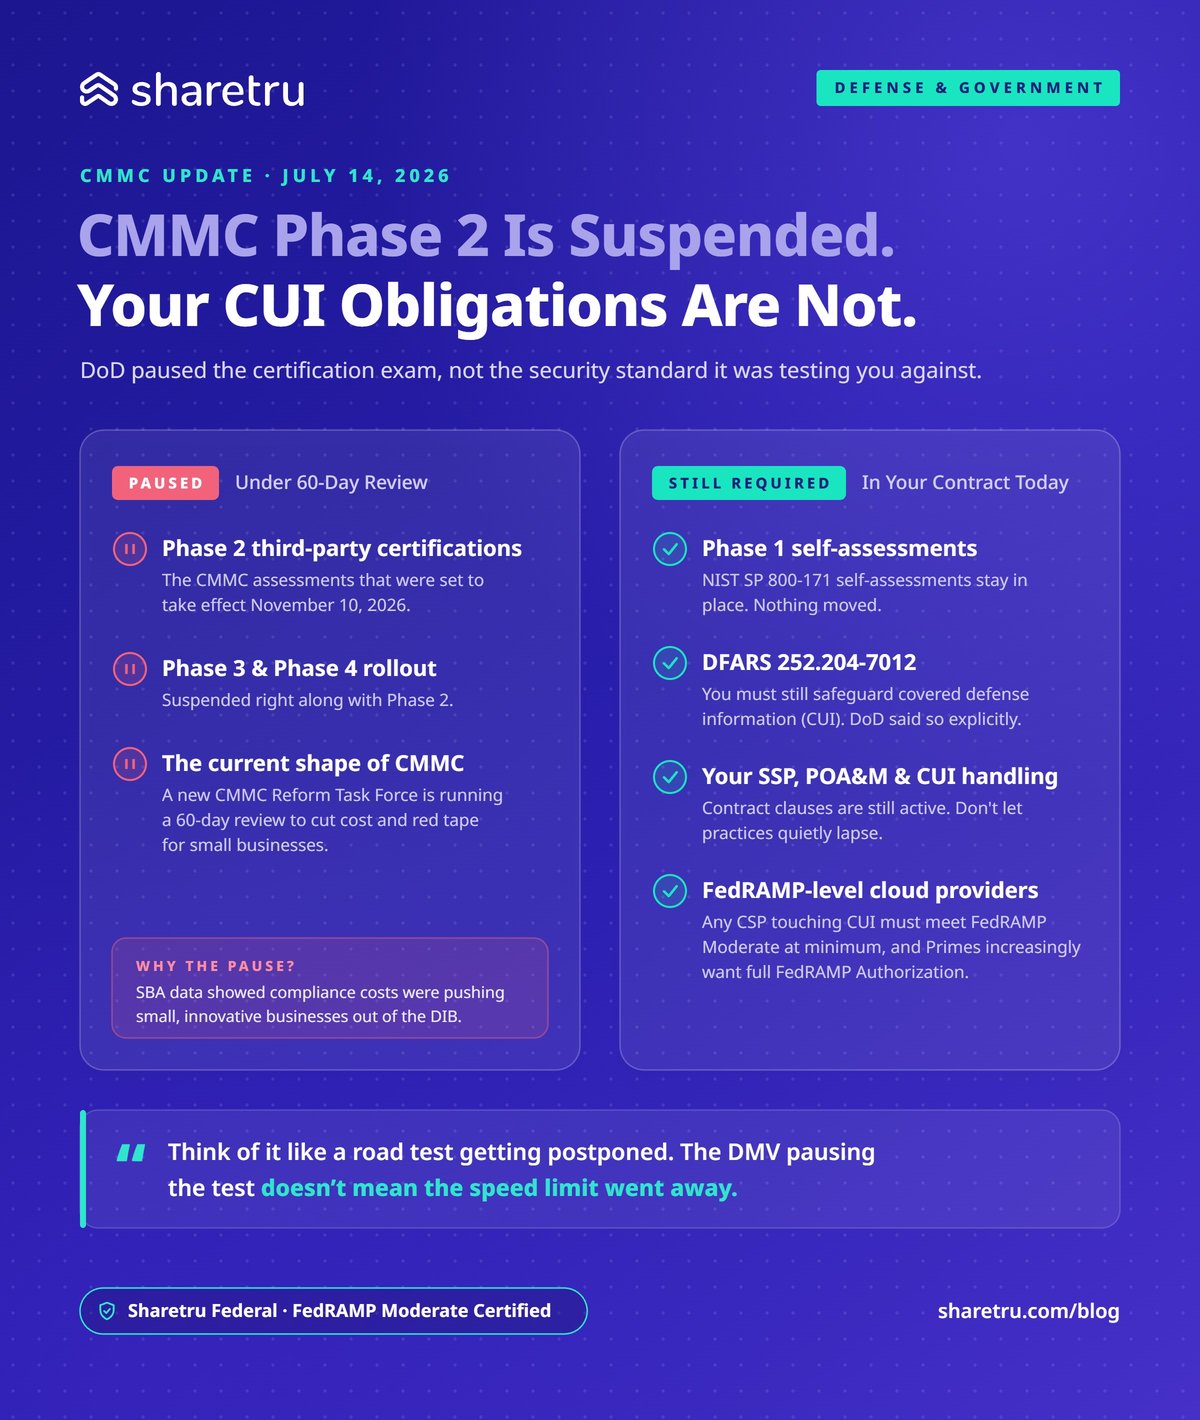
That's why securing CUI now is even more important, not less. Contractors who keep tightening their CUI handling during the pause will be ready for whatever version of CMMC comes next, and they'll have a clear answer when a Prime asks how their CUI is protected. Those who let practices lapse because "CMMC is paused" are taking on contract risk today and a harder climb later.
What's hot and what's not: Matt Travis's take on where CMMC could go
Matt Travis, CEO of The Cyber AB, opened the conference on October 22. One of his slides laid out "what's hot and what's not" in CMMC, and he was clear that it was speculative: his read on where things are trending, not a policy announcement. It's still worth a close look if you're deciding what to do during the pause.
What's hot
- Brilliant at the basics
- Ensuring supply chain resiliency
- Inclusion of operational technology (OT)
- Automation and advanced technology in assessments
- Industrial resilience and supply chain agility
- NIST Cybersecurity Framework (CSF) 2.0 and risk
- Reciprocity with, or advanced standing from, other frameworks
What's not
- CUI is not the highest DIB priority
- Point-in-time certification assessments that go stale
- The "checklist nature" of NIST SP 800-171 Rev 2
- The cost of CMMC implementation and certification
- Over-marking of CUI
- The Risk Management Framework (RMF)
Two things stood out to us.
"Not the highest priority" doesn't mean "not required." Read quickly, "CUI is not the highest DIB priority" can sound like CUI matters less. That isn't the point. On Travis's slide, CUI isn't the biggest problem to solve next. The bigger push is resilience across the whole Defense Industrial Base: supply chain resiliency, operational technology, industrial resilience, and NIST CSF 2.0. However that plays out, protecting the CUI you hold is required today. DFARS 252.204-7012 is still in your contract, and no conference slide changes it. Over-marking made the list too, so the practical takeaway is to mark only what is truly CUI, then handle that information correctly every time it moves.
Point-in-time may be on its way out. Assessments that go stale, the checklist nature of NIST SP 800-171 Rev 2, and the cost of compliance all landed on the "not" list. Being brilliant at the basics, automation in assessments, and reciprocity with other frameworks are hot. If CMMC heads that way after the review, it will reward contractors who can show their controls working every day, with evidence ready on demand, and who don't have to rebuild that evidence for every framework. This is similar to the FedRAMP Moderate requirements regarding continuous monitoring Sharetru must hold itself to. Either way, the pause is the time to tighten how you handle CUI, not loosen it.
Where secure file sharing fits
Defense contractors don't just store Controlled Unclassified Information. They exchange it with primes, subcontractors, and partners every day, and every one of those exchanges needs controls that hold up, whether the reviewer is a C3PAO, a Prime, or your own contracting officer.
Sharetru makes sharing CUI and ITAR data simple, with the controls you need to stay compliant built in from day one. Sharetru Federal is FedRAMP Moderate Certified, not just "FedRAMP equivalent," so you can exchange CUI with primes and subs, share export-controlled technical data, and focus on your mission instead of your file transfer tools.
Missed us at Booth #7? Let's talk.
If securing CUI is on your list, we'd love to show you how Sharetru works. Pick a time that works for you and we'll walk through how Sharetru handles your compliance requirements.
Thanks again to The Cyber AB and everyone who made CS5 East 2026 a great event. We hope to see you at the next one.